Tuesday, October 2, 2012

XSS vulnerability in Parallelus premium WordPress themes

According to my tests, at least the following premium WordPress themes by Parallelus are affected by a reflected Cross-site Scripting (XSS) vulnerability:
Developer status: contact attempt through a web-form, no response. I have also tried to contact two sites using the Unite-theme, but there has been no responses.

Update from the developer: all affected Parallelus themes are now corrected

Screen-shot of the Unite theme XSS vulnerability:

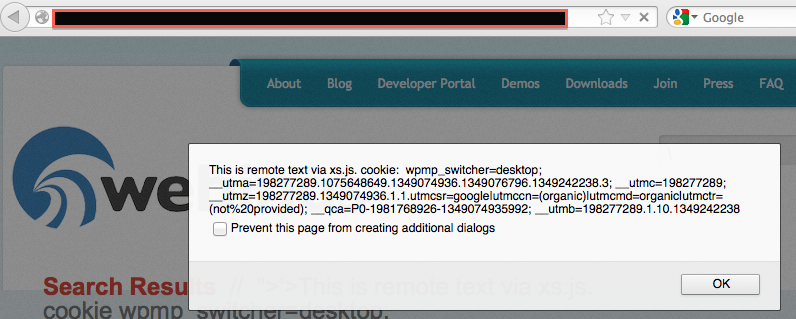
Screen-shot of a website using one of these themes - test case executes a remote Javascript:


Developer's Themeforest profile indicates over 18,000 completed sales, but not all the themes and templates are vulnerable. The number of potentially affected sites could still be high: there has been 4,816 purchases of the Unite-theme alone. Affected sites include personal blogs, but also corporate websites.

I have tested several premium WordPress themes during the last week. The number of found issues is alarming. These cases are challenging from pentesting perspective:
  • identifying potentially affected sites is a big task due to high volumes
  • contacting all affected sites would take too much time
  • many of the developers are difficult to reach and they might consider XSS as a minor issue
Therefore I'm trying to spread information through this blog and Twitter. Please help me if you think it is important to share information especially with the affected sites.

Update 6-Oct-2012 - online references:
F-Secure weblog posting
Threatpost news entry
PC Maganize Securitywatch
OSVDB entries

Monday, October 1, 2012

XSS vulnerability in BigFeature WordPress premium theme

BigFeature WordPress premium theme by Vfxdude is vulnerable to reflected Cross-site Scripting (XSS).

Developer status: notified. Developer response: issue has been fixed

Screen-shot of the XSS test:


Theme upgade is recommended. Theme developer has a support forum and online FAQ.

The number of affected sites is unknown. Themeforest statistics indicates that 4636 purchases have been completed. I tested nine different sites using this theme and they were all affected.

Further reading:
What's Cross-site Scripting -  MakeUseOf-article, July 2012
Why XSS is so serious business a blog post by Troy Hunt, August 2012
The Open Web Application Security Project (OWASP) TOP-10-A2

Saturday, September 29, 2012

XSS vulnerability in multiple premium WordPress themes

According to my tests, the following premium WordPress themes by Flow / Devatic are affeted by a reflected Cross-site Scripting (XSS) vulnerability:
  • Daisho
  • Konzept
  • TheAgency
  • Sparky
  • PictureFactory
  • Paramount
  • Essence
  • Explicit
  • Eunice
  • Blaze
  • Brisk
  • Shapeless
Developer status: notified. Developer response: considered as a minor issue.

Screen-shot of the Blaze theme XSS vulnerability:

 
According to developer's Themeforest profile, 5482 sales have been completed. Potential number of affected customers is however unknown. I tested 26 separate websites using Flow/Devatic themes. Most of the sites are using WordPress version 3.4.x and at least two are using the latest version. All tested sites were vulnerable to reflected Cross-site Scripting.